

Software Defined Security Monitoring in 5G Networks 239
making changes in a device firmware or its hardware. Since the networking devices in
SDN are programmable, changes in networking parameters are comparatively simple.
In SDN, centralization of the control plane would help to avoid inter‐domain conflicts, since the autonomous per‐domain decisions can be monitored by a centralized
monitoring system implemented on top of the control plane, as presented in the previous section.
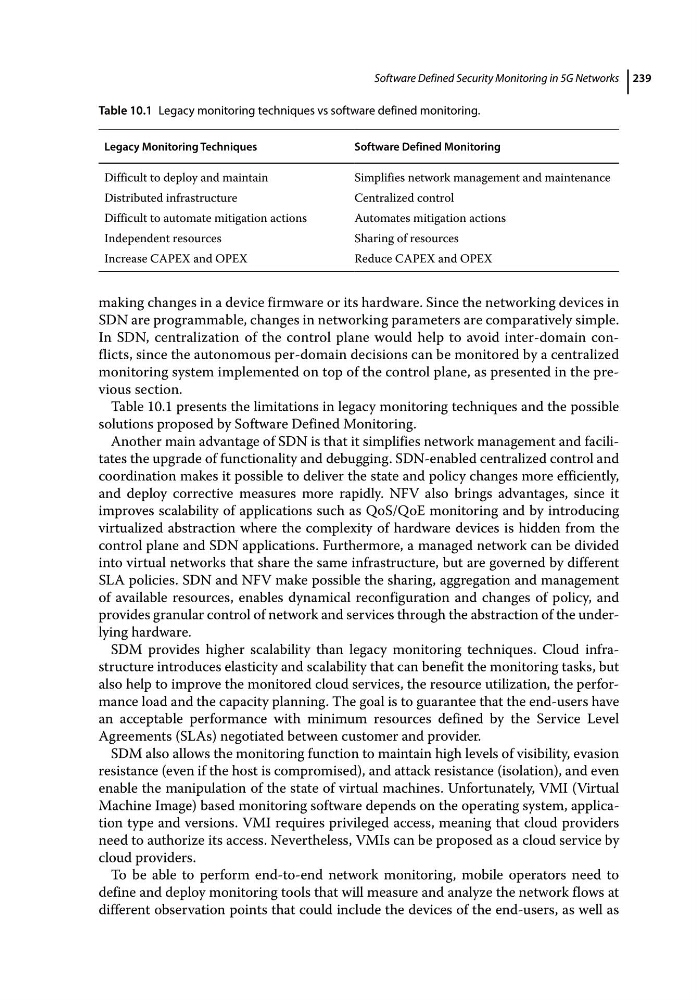
Table 10.1 presents the limitations in legacy monitoring techniques and the possible
solutions proposed by Software Defined Monitoring.
Another main advantage of SDN is that it simplifies network management and facilitates the upgrade of functionality and debugging. SDN‐enabled centralized control and
coordination makes it possible to deliver the state and policy changes more efficiently,
and deploy corrective measures more rapidly. NFV also brings advantages, since it
improves scalability of applications such as QoS/QoE monitoring and by introducing
virtualized abstraction where the complexity of hardware devices is hidden from the
control plane and SDN applications. Furthermore, a managed network can be divided
into virtual networks that share the same infrastructure, but are governed by different
SLA policies. SDN and NFV make possible the sharing, aggregation and management
of available resources, enables dynamical reconfiguration and changes of policy, and
provides granular control of network and services through the abstraction of the underlying hardware.
SDM provides higher scalability than legacy monitoring techniques. Cloud infrastructure introduces elasticity and scalability that can benefit the monitoring tasks, but
also help to improve the monitored cloud services, the resource utilization, the performance load and the capacity planning. The goal is to guarantee that the end‐users have
an acceptable performance with minimum resources defined by the Service Level
Agreements (SLAs) negotiated between customer and provider.
SDM also allows the monitoring function to maintain high levels of visibility, evasion
resistance (even if the host is compromised), and attack resistance (isolation), and even
enable the manipulation of the state of virtual machines. Unfortunately, VMI (Virtual
Machine Image) based monitoring software depends on the operating system, application type and versions. VMI requires privileged access, meaning that cloud providers
need to authorize its access. Nevertheless, VMIs can be proposed as a cloud service by
cloud providers.
To be able to perform end‐to‐end network monitoring, mobile operators need to
define and deploy monitoring tools that will measure and analyze the network flows at
different observation points that could include the devices of the end‐users, as well as
Table 10.1 Legacy monitoring techniques vs software defined monitoring.
Legacy Monitoring Techniques
Software Defined Monitoring
Difficult to deploy and maintain
Simplifies network management and maintenance
Distributed infrastructure
Centralized control
Difficult to automate mitigation actions
Automates mitigation actions
Independent resources
Sharing of resources
Increase CAPEX and OPEX
Reduce CAPEX and OPEX