

5.2 Decoy-State Method
75
8] and that recently it was shown that the BB84 protocol can also be implemented
with just one decoy intensity setting [9].
From the first set of equations (5.9) one derives lower bounds Y
0↓ and Y
1↓
Z which
correspond to lower bounds on the quantities Q
0 and Q
1
Z appearing in the key rate
(5.4). From the second set (5.10), one derives bounds on the yields that are then
employed in the third set (5.11) to derive the upper bound e
1↑
X .
Let us briefly sum up the implementation of the asymmetric BB84 protocol with
the integration of the decoy-state method. Alice prepares phase-randomized WCPs
polarized in the Z (X ) basis with probability p Z (1 − p Z ). Upon choosing the Z
basis, she modulates the pulse intensity to μ with probability q to generate a signal
state, or to one of the decoy intensities {μ i } to generate a decoy state with probability
1 − q. If Alice picks the X basis instead, she only generates decoy states. Bob chooses
to measure the incoming pulse in the Z (X ) basis with probability p Z (1 − p Z ).
At the end of the transmission, Alice reveals the intensity setting and the basis
she used in every round. Bob instead reveals all the X outcomes to estimate E
μ i
X and
some of the Z outcomes of the signal state to estimate E
μ
Z .
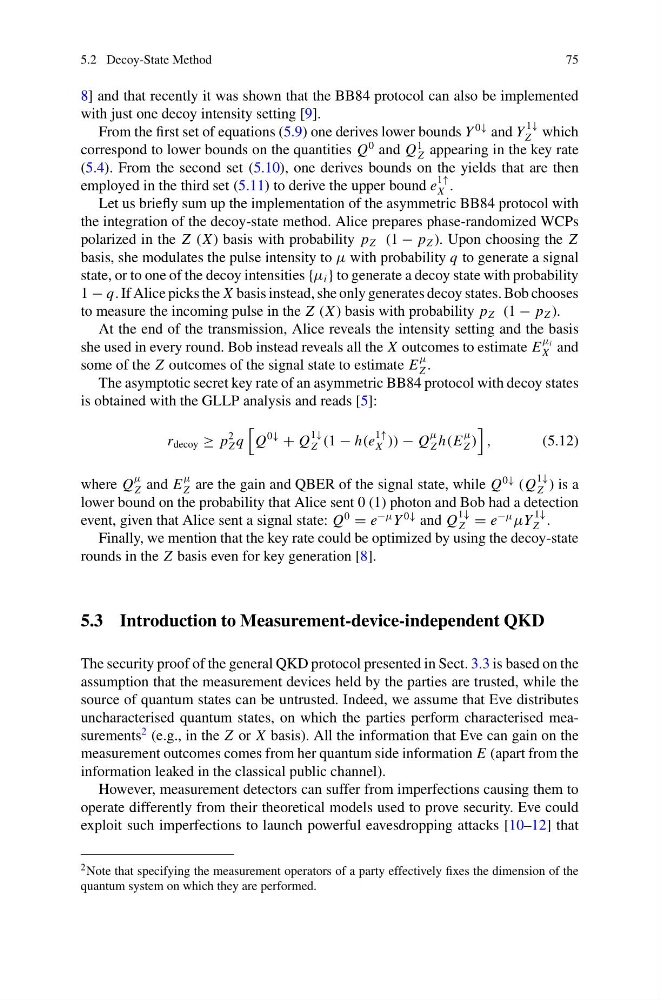
The asymptotic secret key rate of an asymmetric BB84 protocol with decoy states
is obtained with the GLLP analysis and reads [5]:
r decoy ≥ p
2
Z q
Q
0↓
+ Q
1↓
Z (1 − h(e
1↑
X )) − Q
μ
Z h(E
μ
Z )
,
(5.12)
where Q
μ
Z and E
μ
Z are the gain and QBER of the signal state, while Q
0↓ (Q
1↓
Z ) is a
lower bound on the probability that Alice sent 0 (1) photon and Bob had a detection
event, given that Alice sent a signal state: Q
0
= e
−μ Y
0↓ and Q
1↓
Z = e
−μ
μY
1↓
Z .
Finally, we mention that the key rate could be optimized by using the decoy-state
rounds in the Z basis even for key generation [8].
5.3 Introduction to Measurement-device-independent QKD
The security proof of the general QKD protocol presented in Sect. 3.3 is based on the
assumption that the measurement devices held by the parties are trusted, while the
source of quantum states can be untrusted. Indeed, we assume that Eve distributes
uncharacterised quantum states, on which the parties perform characterised measurements
2 (e.g., in the Z or X basis). All the information that Eve can gain on the
measurement outcomes comes from her quantum side information E (apart from the
information leaked in the classical public channel).
However, measurement detectors can suffer from imperfections causing them to
operate differently from their theoretical models used to prove security. Eve could
exploit such imperfections to launch powerful eavesdropping attacks [10–12] that
2 Note that specifying the measurement operators of a party effectively fixes the dimension of the
quantum system on which they are performed.