

6.5 Conference Key Agreement with Single Photon Interference
101
phase introduced by the BS in the shared state (6.38) reduces to a minus sign, which
can be reabsorbed by asking Alice 2 to flip her classical outcome b 2 when detector
D 2 clicks, as described in Sect. 6.3.1. This removes the need to adjust the parties’
measurements depending on the result of the detection, hence making these two steps
commute.
Nevertheless, the quantum operations of the CKA scheme in [26] seem to be
feasible with present-day technology. In particular, the parties’ qubits may be realized
with electronic spin-1 systems of nitrogen-vacancy (NV) centres in diamond [33, 34],
characterized by second-long coherence times [35]. This would allow the parties to
delay the measurements on their qubits until the relay announces which detectors
clicked, as requested by the CKA protocol. Moreover, the qubit state can be accurately
tuned by shining microwave pulses and can be subsequently entangled to the photon
number (presence or absence of a photon) by exciting its ground state, which then
spontaneously emits a photon [33]. This process realizes the qubit-photon entangled
state (6.32).
6.5.2 Performance Assessment
In [26], we prove the CKA security in the finite-key scenario for the most general
attacks the eavesdropper can perform. We also investigate the protocol’s performance
for a realistic channel model that accounts for polarization and phase misalignments
and dark counts in the detectors.
In order to benchmark the performance of our CKA based on a central untrusted
relay, we consider a scenario where the relay is removed and the parties are all connected in a star network where the transmittance between any two parties is η. In
this configuration, we consider the conference key rate generated by the following
strategy and compare it with the CKA key rate (6.37). One special party, say Alice 1 ,
performs the best possible bipartite QKD protocol with every other party, thus establishing N − 1 secret keys whose key rate is given by the PLOB bound (6.1). Alice 1
then uses the established keys to distribute the conference key to the other parties
with one-time pad encryption. The resulting conference key rate is thus given by the
rate at which the bipartite keys were generated, rescaled by the factor 1/(N − 1)
which accounts for the fact that Alice 1 repeated the bipartite scheme N − 1 times.
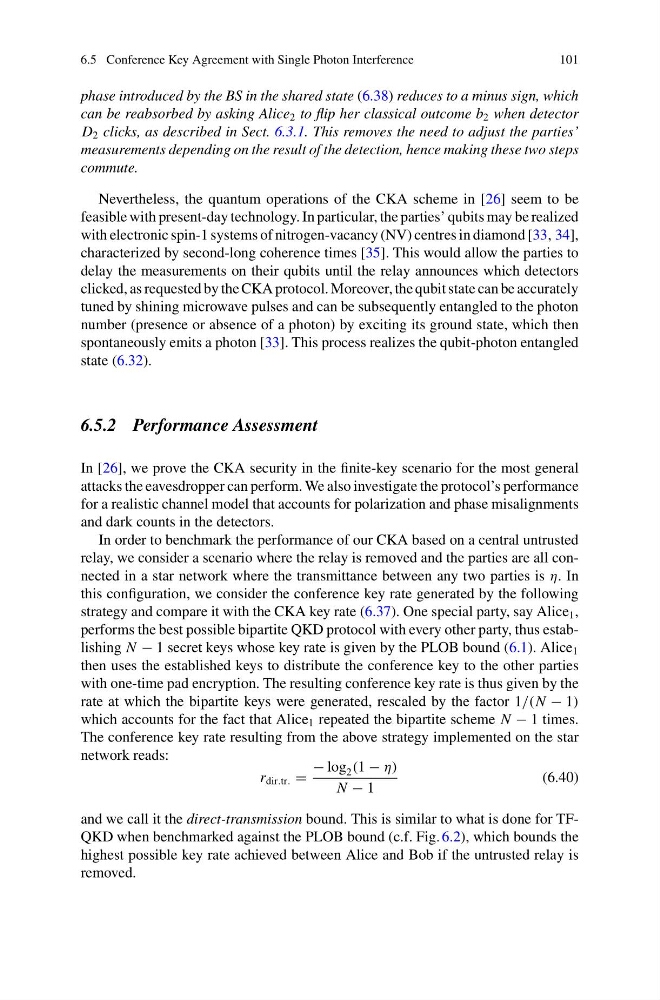
The conference key rate resulting from the above strategy implemented on the star
network reads:
r dir.tr. =
− log 2 (1 − η)
N − 1
(6.40)
and we call it the direct-transmission bound. This is similar to what is done for TFQKD when benchmarked against the PLOB bound (c.f. Fig. 6.2), which bounds the
highest possible key rate achieved between Alice and Bob if the untrusted relay is
removed.