

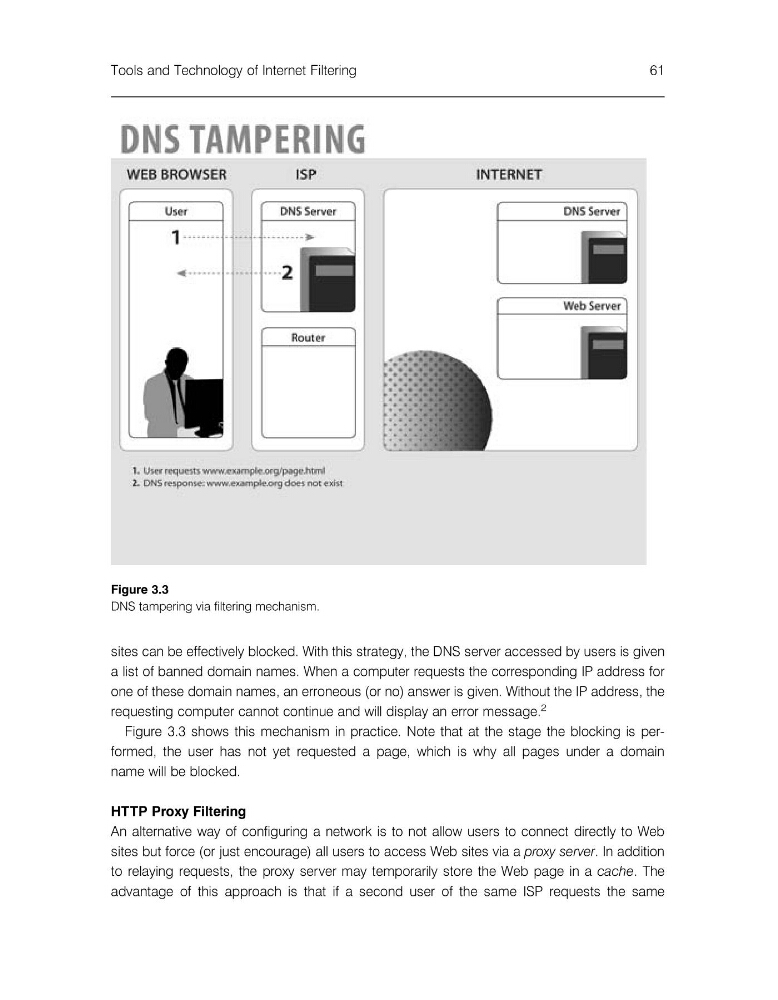
sites can be effectively blocked. With this strategy, the DNS server accessed by users is given
a list of banned domain names. When a computer requests the corresponding IP address for
one of these domain names, an erroneous (or no) answer is given. Without the IP address, the
requesting computer cannot continue and will display an error message.
2
Figure 3.3 shows this mechanism in practice. Note that at the stage the blocking is performed, the user has not yet requested a page, which is why all pages under a domain
name will be blocked.
HTTP Proxy Filtering
An alternative way of configuring a network is to not allow users to connect directly to Web
sites but force (or just encourage) all users to access Web sites via a proxy server. In addition
to relaying requests, the proxy server may temporarily store the Web page in a cache. The
advantage of this approach is that if a second user of the same ISP requests the same
Figure 3.3
DNS tampering via filtering mechanism.
Tools and Technology of Internet Filtering
61