

have a maximum size, the full content of the communication will likely be split over multiple
packets. Thus while the offending packet will get through, the communication can be disrupted by blocking subsequent packets. This may be achieved by blocking the packets
directly or by sending a message to both of the communicating parties requesting they terminate the conversation.
1
Another effect of the maximum packet size is that keywords may be split over packet
boundaries. Devices that inspect each packet individually may then fail to identify infringing
keywords. For packet inspection to be fully effective, the stream must be reassembled, which
adds additional complexity. Alternatively, an HTTP proxy filter can be used, as described later.
DNS Tampering
Most Internet communication uses domain names rather than IP addresses, particularly for
Web browsing. Thus, if the domain name resolution stage can be filtered, access to infringing
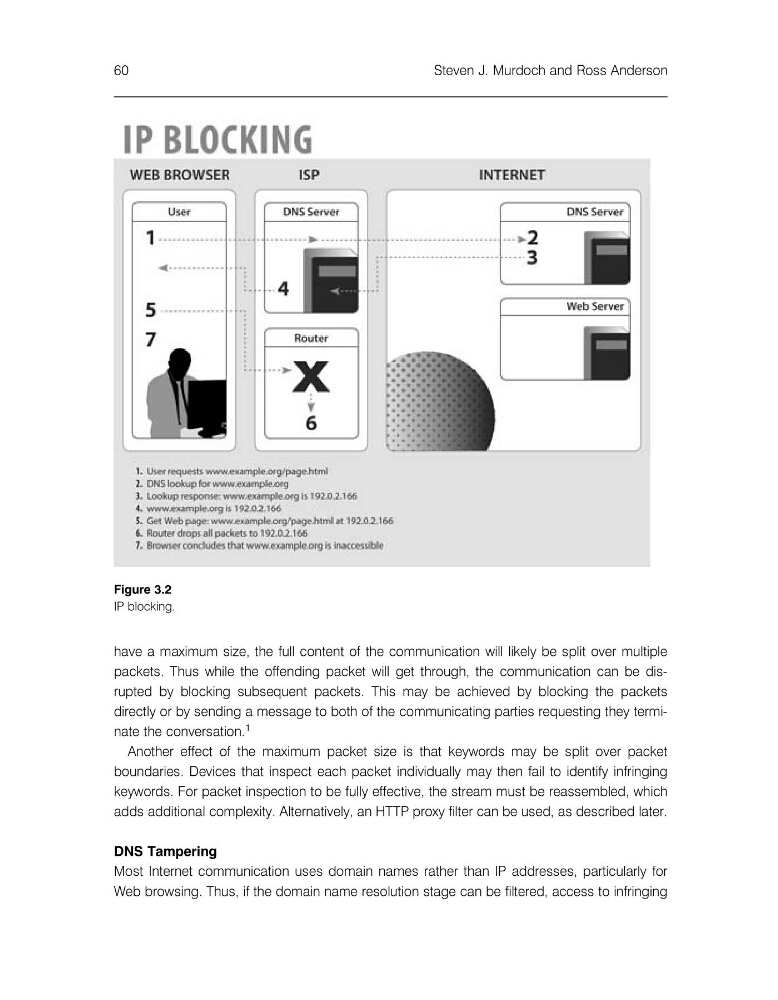
Figure 3.2
IP blocking.
60
Steven J. Murdoch and Ross Anderson