

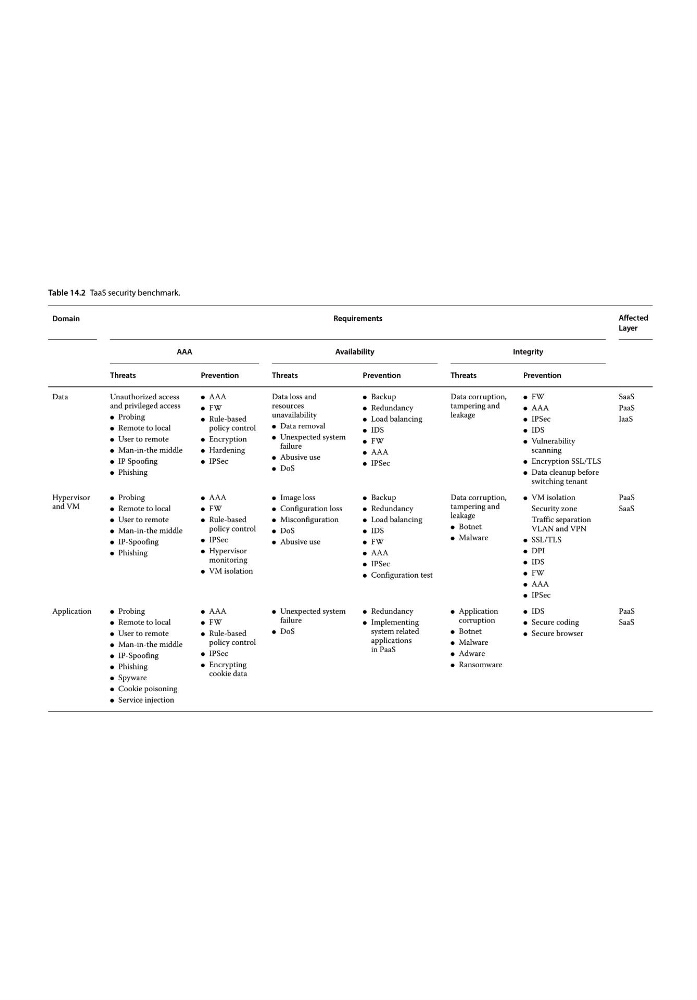
Table 14.2 TaaS security benchmark.
Domain
Requirements
Affected
Layer
AAA
Availability
I ntegrity
Threats
P revention
Threats
P revention
Threats
P revention
Data
Unauthorized access
and privileged access
● Probing
● Remote to local
● User to remote
● Man‐in‐the middle
● IP Spoofing
● Phishing
● AAA
● FW
● Rule‐based
policy control
● Encryption
● Hardening
● IPSec
Data loss and
resources
unavailability
● Data removal
● Unexpected system
failure
● Abusive use
● DoS
● Backup
● Redundancy
● Load balancing
● IDS
● FW
● AAA
● IPSec
Data corruption,
tampering and
leakage
● FW
● AAA
● IPSec
● IDS
● Vulnerability
scanning
● Encryption SSL/TLS
● Data cleanup before
switching tenant
SaaS
PaaS
IaaS
Hypervisor
and VM
● Probing
● Remote to local
● User to remote
● Man‐in‐the middle
● IP‐Spoofing
● Phishing
● AAA
● FW
● Rule‐based
policy control
● IPSec
● Hypervisor
monitoring
● VM isolation
● Image loss
● Configuration loss
● Misconfiguration
● DoS
● Abusive use
● Backup
● Redundancy
● Load balancing
● IDS
● FW
● AAA
● IPSec
● Configuration test
Data corruption,
tampering and
leakage
● Botnet
● Malware
● VM isolation
Security zone
Traffic separation
VLAN and VPN
● SSL/TLS
● DPI
● IDS
● FW
● AAA
● IPSec
PaaS
SaaS
Application
● Probing
● Remote to local
● User to remote
● Man‐in‐the middle
● IP‐Spoofing
● Phishing
● Spyware
● Cookie poisoning
● Service injection
● AAA
● FW
● Rule‐based
policy control
● IPSec
● Encrypting
cookie data
● Unexpected system
failure
● DoS
● Redundancy
● Implementing
system related
applications
in PaaS
● Application
corruption
● Botnet
● Malware
● Adware
● Ransomware
● IDS
● Secure coding
● Secure browser
PaaS
SaaS