

Monshizadeh and Khatri
334
14.4.4 Summary
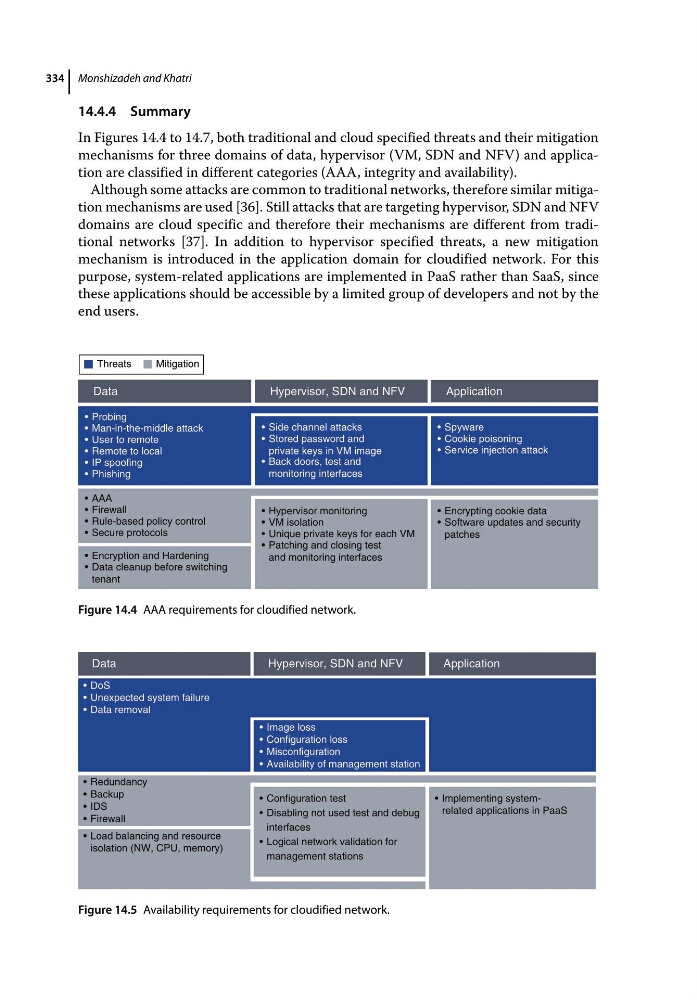
In Figures 14.4 to 14.7, both traditional and cloud specified threats and their mitigation
mechanisms for three domains of data, hypervisor (VM, SDN and NFV) and application are classified in different categories (AAA, integrity and availability).
Although some attacks are common to traditional networks, therefore similar mitigation mechanisms are used [36]. Still attacks that are targeting hypervisor, SDN and NFV
domains are cloud specific and therefore their mechanisms are different from traditional networks [37]. In addition to hypervisor specified threats, a new mitigation
mechanism is introduced in the application domain for cloudified network. For this
purpose, system‐related applications are implemented in PaaS rather than SaaS, since
these applications should be accessible by a limited group of developers and not by the
end users.
Data
Hypervisor, SDN and NFV
Application
• Probing
• Man-in-the-middle attack
• User to remote
• Remote to local
• IP spoofing
• Phishing
• Spyware
• Cookie poisoning
• Service injection attack
• AAA
• Firewall
• Rule-based policy control
• Secure protocols
• Encryption and Hardening
• Data cleanup before switching
tenant
• Encrypting cookie data
• Software updates and security
patches
Threats
Mitigation
• Side channel attacks
• Stored password and
private keys in VM image
• Back doors, test and
monitoring interfaces
• Hypervisor monitoring
• VM isolation
• Unique private keys for each VM
• Patching and closing test
and monitoring interfaces
Figure 14.4 AAA requirements for cloudified network.
• Implementing systemrelated applications in PaaS
• Image loss
• Configuration loss
• Misconfiguration
• Availability of management station
Data
Hypervisor, SDN and NFV
Application
• Configuration test
• Disabling not used test and debug
interfaces
• Logical network validation for
management stations
• DoS
• Unexpected system failure
• Data removal
• Redundancy
• Backup
• IDS
• Firewall
• Load balancing and resource
isolation (NW, CPU, memory)
Figure 14.5 Availability requirements for cloudified network.