

Customer Edge Switching: A Security Framework for 5G 223
For example, in the case of 5G mobile networks, the CES function can be deployed
as part of the gateway application that provides connectivity to the Internet and other
public data networks. This effectively complements the functions currently performed
by the Packet Data Gateway (PGW) in 3GPP networks. Since 5G core network will be
expectedly defined and controlled by a set of virtualized network applications,
we developed a demonstrator of the 5G‐network control plane using a set of SDN
applications [22], where CES serves as the access provisioning application. The dem‑
onstrator carried the traffic between LTE user devices and the Internet via an eNodeB
supplied by Nokia.
The deployment of the proposed CES framework as a part of 5G, or other 3GPP
mobile networks, can provide enhanced traffic management by eliminating a part of
unwanted traffic. This can be initially done in a specific slice of the 5G EPC carrying
ultra‐reliable services. In the long run, there is good motivation to integrate CES with
all PGWs in mobile networks.
For instance, by using existing control nodes and seeking policy requests, CES can
collect sufficient information from a source to establish its legitimacy. CES allows users,
hosts and applications to define their reachability policies and hence control the traffic
they deem interesting. Therefore, the contribution of CES to the future networks can
be in reducing or eliminating malicious traffic from being a cause of failure to the
legitimate services, and thus contributing to ultra‐high reliability of services in 5G. CES
adheres to the SDN‐principles and can be leveraged in other networks also, for example
for providing access to objects in the Industrial Internet or Internet of Things (IoT). For
deployment into corporate network gateways, CES functionality needs to be integrated
into firewall products. Compared to various tunnelling proposals that focus on solving
the core scalability issues in the Future Internet, CES is focused on trust and in providing
added value to end customers as a result of the improved security.
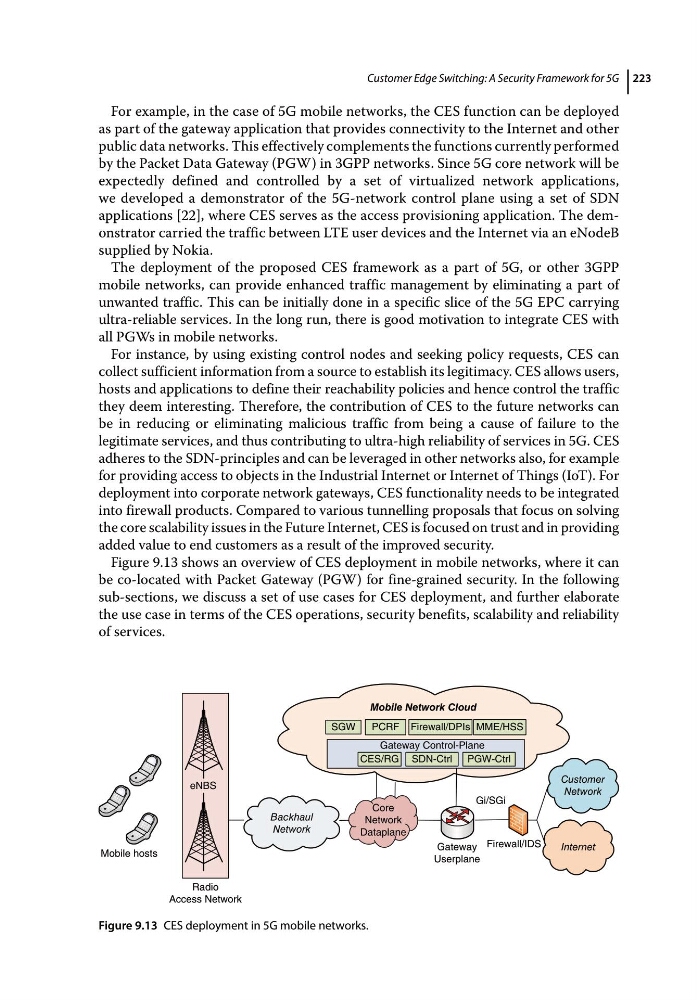
Figure 9.13 shows an overview of CES deployment in mobile networks, where it can
be co‐located with Packet Gateway (PGW) for fine‐grained security. In the following
sub‐sections, we discuss a set of use cases for CES deployment, and further elaborate
the use case in terms of the CES operations, security benefits, scalability and reliability
of services.
Mobile hosts
Gateway
Userplane
Gateway Control-Plane
Core
Network
Dataplane
CES/RG SDN-Ctrl PGW-Ctrl
SGW
PCRF Firewall/DPIs MME/HSS
Firewall/IDS
Gi/SGi
eNBS
Radio
Access Network
Backhaul
Network
Internet
Customer
Network
Mobile Network Cloud
Figure 9.13 CES deployment in 5G mobile networks.