

5G-WLAN Security 153
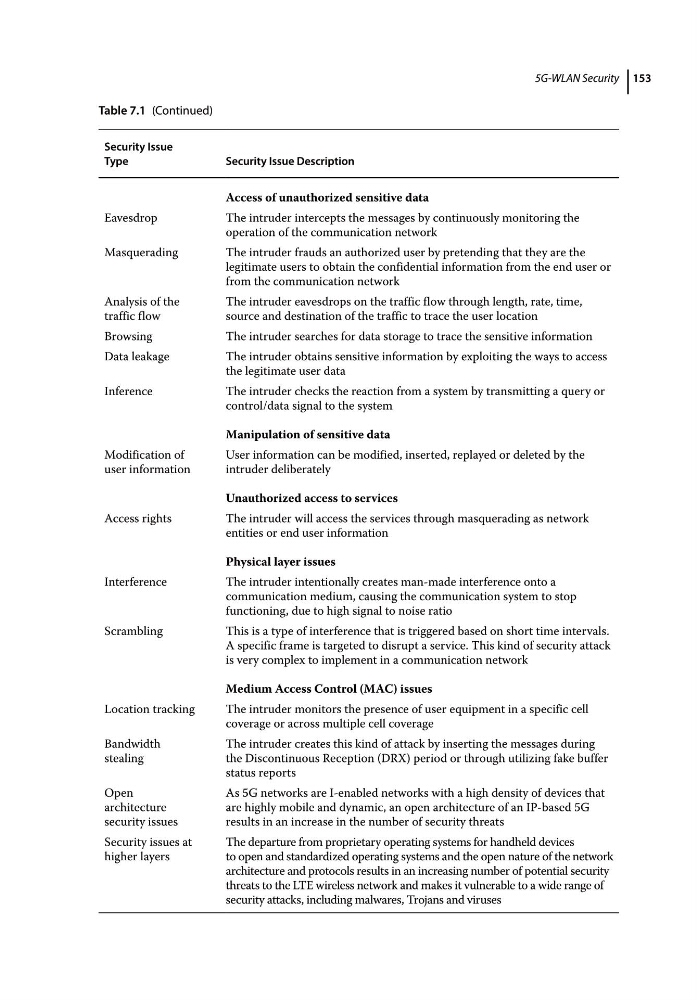
Table 7.1 (Continued)
Security Issue
Type
Security Issue Description
Access of unauthorized sensitive data
Eavesdrop
The intruder intercepts the messages by continuously monitoring the
operation of the communication network
Masquerading
The intruder frauds an authorized user by pretending that they are the
legitimate users to obtain the confidential information from the end user or
from the communication network
Analysis of the
traffic flow
The intruder eavesdrops on the traffic flow through length, rate, time,
source and destination of the traffic to trace the user location
Browsing
The intruder searches for data storage to trace the sensitive information
Data leakage
The intruder obtains sensitive information by exploiting the ways to access
the legitimate user data
Inference
The intruder checks the reaction from a system by transmitting a query or
control/data signal to the system
Manipulation of sensitive data
Modification of
user information
User information can be modified, inserted, replayed or deleted by the
intruder deliberately
Unauthorized access to services
Access rights
The intruder will access the services through masquerading as network
entities or end user information
Physical layer issues
Interference
The intruder intentionally creates man‐made interference onto a
communication medium, causing the communication system to stop
functioning, due to high signal to noise ratio
Scrambling
This is a type of interference that is triggered based on short time intervals.
A specific frame is targeted to disrupt a service. This kind of security attack
is very complex to implement in a communication network
Medium Access Control (MAC) issues
Location tracking
The intruder monitors the presence of user equipment in a specific cell
coverage or across multiple cell coverage
Bandwidth
stealing
The intruder creates this kind of attack by inserting the messages during
the Discontinuous Reception (DRX) period or through utilizing fake buffer
status reports
Open
architecture
security issues
As 5G networks are I‐enabled networks with a high density of devices that
are highly mobile and dynamic, an open architecture of an IP‐based 5G
results in an increase in the number of security threats
Security issues at
higher layers
The departure from proprietary operating systems for handheld devices
to open and standardized operating systems and the open nature of the network
architecture and protocols results in an increasing number of potential security
threats to the LTE wireless network and makes it vulnerable to a wide range of
security attacks, including malwares, Trojans and viruses