

4.1 Extending QKD to Multiple Parties
59
Remark 4.2 (Preshared key) The parties can know beforehand the classification of
each round of the protocol thanks to a preshared secret key they hold. For instance,
they could share a key with as many bits as rounds, where the bit value 1 (0) indicates
a PE (KG) round. Let us call p e the probability that a PE round is performed. Since
p e is typically small, the key is mainly composed of zeroes and can thus be highly
compressed. In particular, being M the total number of rounds, the parties need a
preshared secret key of M h( p e ) bits, where h(x) is the binary entropy (c.f. Chap. 2).
The length of the preshared key must be subtracted from the final secret key length in
order to quantify the amount of fresh secret bits produced by the protocol. However,
in the asymptotic regime (M → ∞), the penalty introduced by the preshared key
on the asymptotic conference key rate is given by h( p e ) and is negligible, e.g. by
choosing p e ∼ 1/M.
In order to know the length of the secret key that can be extracted by PA, the
parties need to quantify the smooth min-entropy of Alice’s raw key Z
n
A conditioned
on Eve’s information E (Sect. 2.10), where we emphasized that the raw keys are
obtained from Z -basis measurements.
In [13] the min-entropy H
ε
min (Z
n
A |E) is bounded as a function of E X , which is
computed in the PE step. This is possible thanks to the uncertainty relation for smooth
entropies [24]. The uncertainty relation states that, given the state ρ
n
AB 1 ...B N −1 E of the
n rounds yielding the raw keys and assuming that Alice measures her n qubits in
either the Z or X basis, it holds:
H
ε
min (Z
n
A |E) ≥ q − H
ε
max (X
n
A |B 1 . . . B N −1 ),
(4.3)
where X
n
A represents the outcomes Alice would obtain had she measured the n
KG rounds in the X basis. The term q accounts for the incompatibility of the two
measurements of Alice (see [24] for a formal definition). In our case, since Alice
measures each qubit either in the Z or X basis, it reads: q = n for n KG rounds.
Thanks to the data-processing inequality (2.66), we can lower bound the r.h.s. of
(4.3). Specifically, we assume that every Bob measures his qubit in the X basis in each
of the n KG rounds. Thus each Bob B i obtains a string of X outcomes denoted X
n
B i
.
We then multiply element by element the strings of X outcomes of every Bob and
obtain X
n
B =
N −1
i=1 X
n
B i
. The data-processing inequality states that the uncertainty
of the Bobs about X
n
A , quantified by H
ε
max (X
n
A |B 1 . . . B N −1 ), can only increase if they
process their quantum side information in the way we described. This leads to:
H
ε
min (Z
n
A |E) ≥ n − H
ε
max (X
n
A |X
n
B ).
(4.4)
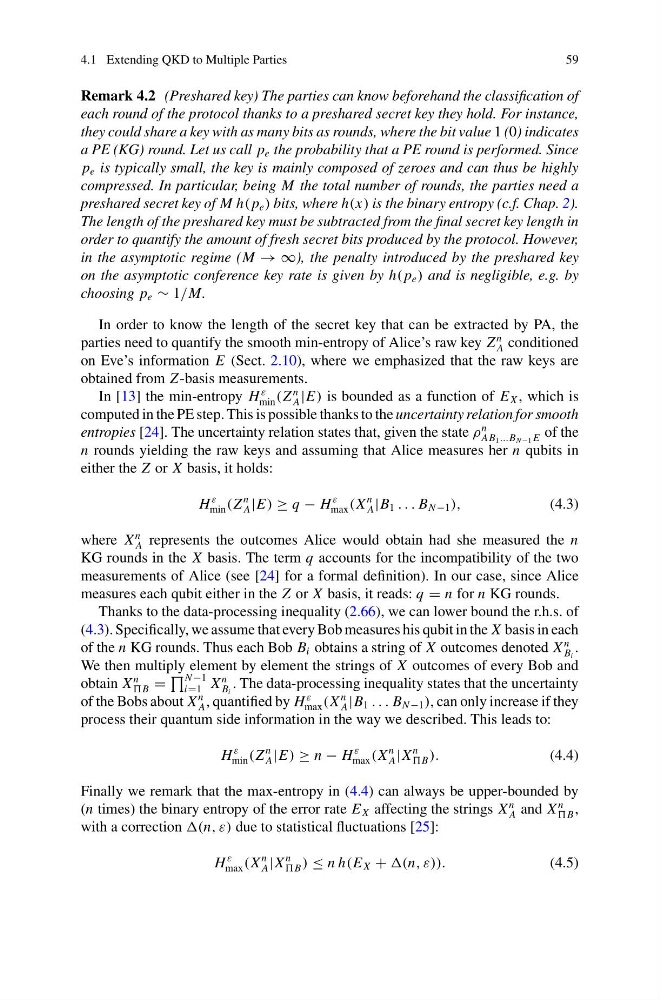
Finally we remark that the max-entropy in (4.4) can always be upper-bounded by
(n times) the binary entropy of the error rate E X affecting the strings X
n
A and X
n
B ,
with a correction (n, ε) due to statistical fluctuations [25]:
H
ε
max (X
n
A |X
n
B ) ≤ n h(E X + (n, ε)).
(4.5)