

696
7 Countermeasures Against Hardware Trojans
(d) Hardware memory isolation. Here, all untrusted IPs are provided with their
separate segments of isolated system resources within the limits of this specific
separate sandbox, extracting all standard mechanisms of memory access security
verification from the sandbox manager and focusing only on data transmission
between separate involved memory segments in the sandbox and the rest of the
system.
7.5.6 Typical Structure of a Hardware Sandbox
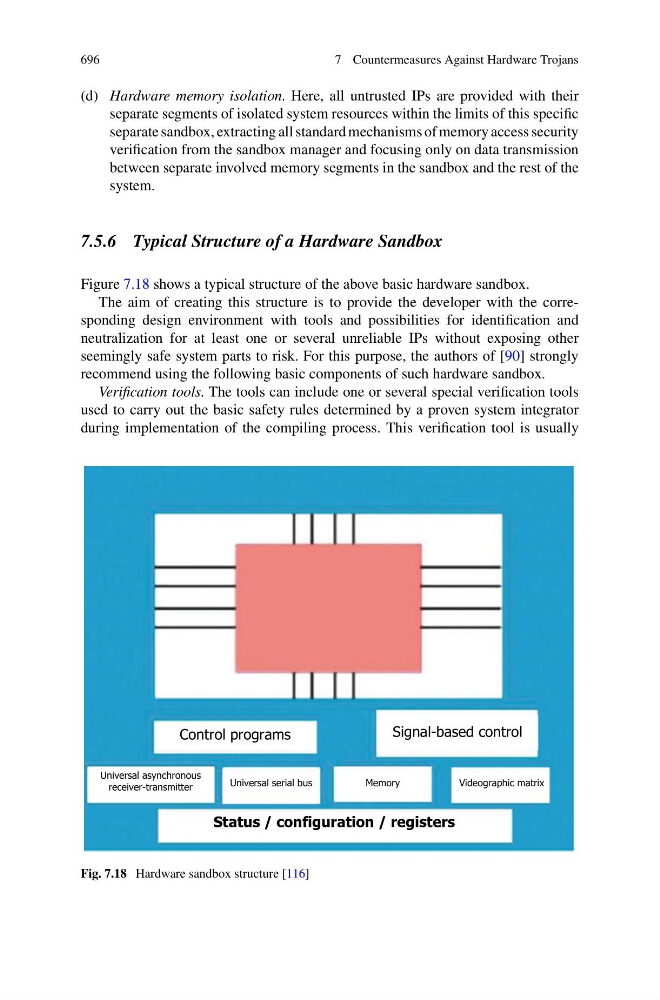
Figure 7.18 shows a typical structure of the above basic hardware sandbox.
The aim of creating this structure is to provide the developer with the corresponding design environment with tools and possibilities for identification and
neutralization for at least one or several unreliable IPs without exposing other
seemingly safe system parts to risk. For this purpose, the authors of [90] strongly
recommend using the following basic components of such hardware sandbox.
Verification tools. The tools can include one or several special verification tools
used to carry out the basic safety rules determined by a proven system integrator
during implementation of the compiling process. This verification tool is usually
Control programs
Signal-based control
Status / configuration / registers
Universal asynchronous
receiver-transmitter
Universal serial bus
Memory
Videographic matrix
Fig. 7.18 Hardware sandbox structure [116]