

222
3 Hardware Trojans in Electronic Devices
Let us consider in detail the methods of protection from unknown keyloggers or
keyloggers designed for attacking a specific system.
Here, a few words need to be said about methodology of security. As the main
goal of any keyloggers is acquisition of confidential information (bank card numbers,
passwords, etc.), the reasonable protection methods are as follows:
– The use of one-time passwords/two-factor authentication;
– The use of proactive protection systems;
– The use of virtual keyboards;
– The use of no-script extensions for browsers.
A one-time password can only be used once; at the same time, the period of time
during which it can be used is also often limited.
Therefore, even if such password is intercepted, the intruder will not be able to
use it to access confidential information.
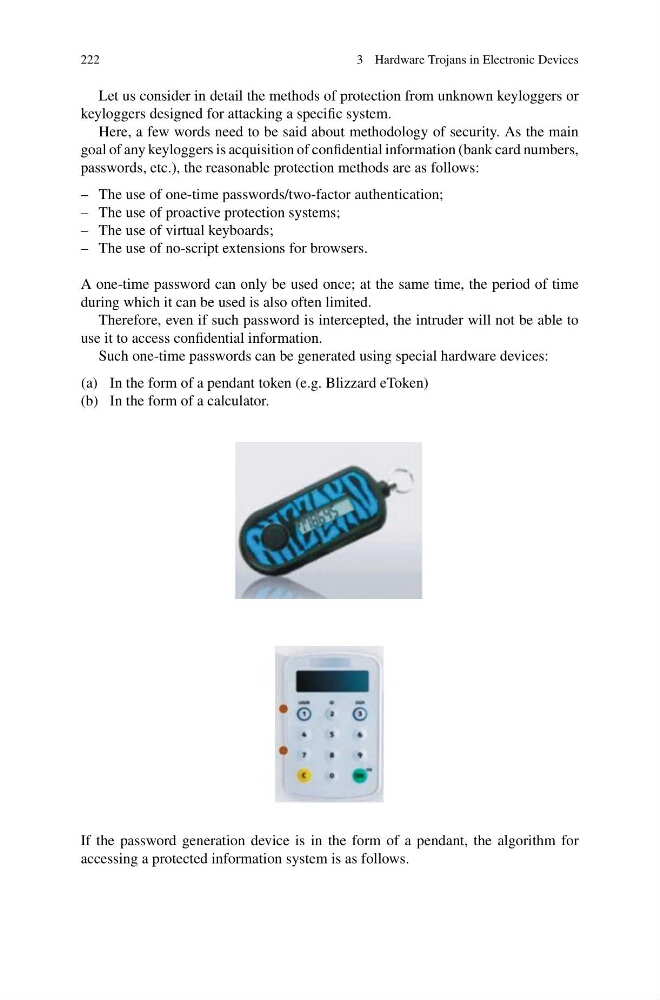
Such one-time passwords can be generated using special hardware devices:
(a) In the form of a pendant token (e.g. Blizzard eToken)
(b) In the form of a calculator.
If the password generation device is in the form of a pendant, the algorithm for
accessing a protected information system is as follows.