

3.2 Hardware Trojans in Computers
217
GINSU Trojan is the Trojan part of the complex including the hardware implant
BULLDOZER (installed in the PCI connector) and the software implant KONGUR.
In combination, it provides remote access to Windows systems.
MAESTRO-II Trojan is an IC-based module that can be easily configured for
performance of specific tasks.
IRATEMONK Trojan is a malicious code in firmware of hard disk drives from the
following manufacturers: Western Digital, Seagate, Maxtor, and Samsung. It allows
replacing Master Boot Record (MBR).
SWAP Trojan is a malicious code in the BIOS firmware that allows implementing
remote control of various operating systems (Windows, FreeBSD, Linux, and Solaris)
and file systems (FAT32, NTFS, EXT2, EXT3, and UFS 1.0) on the user’s computer.
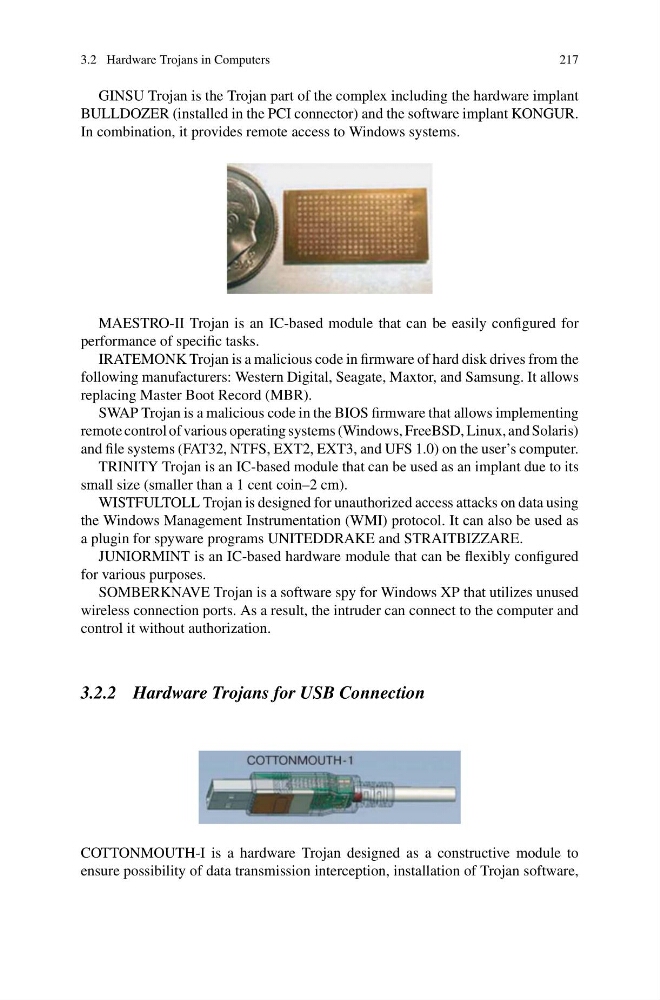
TRINITY Trojan is an IC-based module that can be used as an implant due to its
small size (smaller than a 1 cent coin–2 cm).
WISTFULTOLL Trojan is designed for unauthorized access attacks on data using
the Windows Management Instrumentation (WMI) protocol. It can also be used as
a plugin for spyware programs UNITEDDRAKE and STRAITBIZZARE.
JUNIORMINT is an IC-based hardware module that can be flexibly configured
for various purposes.
SOMBERKNAVE Trojan is a software spy for Windows XP that utilizes unused
wireless connection ports. As a result, the intruder can connect to the computer and
control it without authorization.
3.2.2 Hardware Trojans for USB Connection
COTTONMOUTH-I is a hardware Trojan designed as a constructive module to
ensure possibility of data transmission interception, installation of Trojan software,