

2.6 Cookies Spyware
177
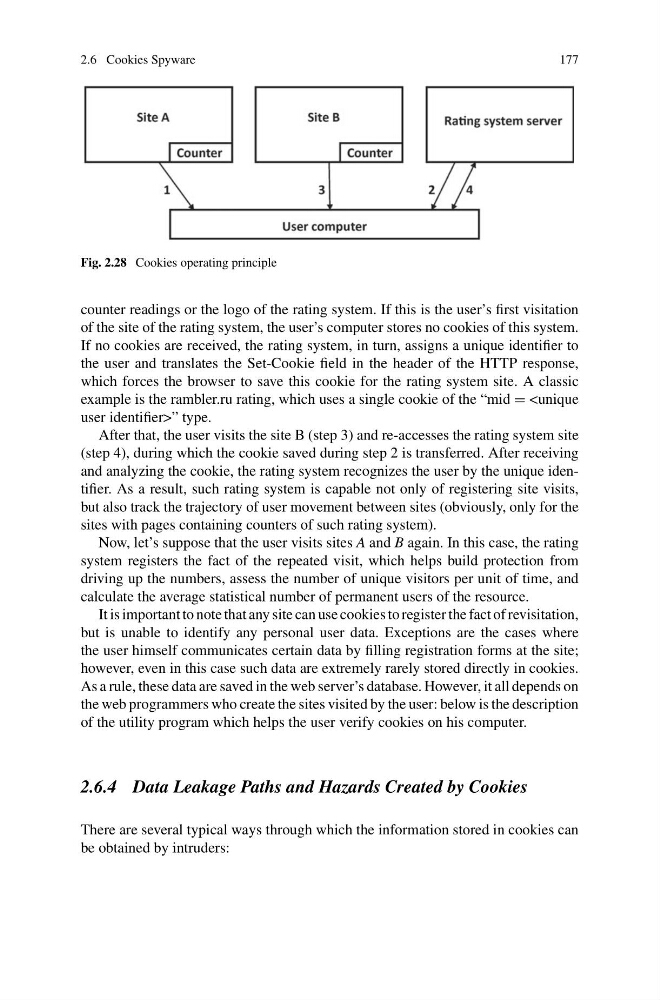
Fig. 2.28 Cookies operating principle
counter readings or the logo of the rating system. If this is the user’s first visitation
of the site of the rating system, the user’s computer stores no cookies of this system.
If no cookies are received, the rating system, in turn, assigns a unique identifier to
the user and translates the Set-Cookie field in the header of the HTTP response,
which forces the browser to save this cookie for the rating system site. A classic
example is the rambler.ru rating, which uses a single cookie of the “mid =
After that, the user visits the site B (step 3) and re-accesses the rating system site
(step 4), during which the cookie saved during step 2 is transferred. After receiving
and analyzing the cookie, the rating system recognizes the user by the unique identifier. As a result, such rating system is capable not only of registering site visits,
but also track the trajectory of user movement between sites (obviously, only for the
sites with pages containing counters of such rating system).
Now, let’s suppose that the user visits sites A and B again. In this case, the rating
system registers the fact of the repeated visit, which helps build protection from
driving up the numbers, assess the number of unique visitors per unit of time, and
calculate the average statistical number of permanent users of the resource.
It is important to note that any site can use cookies to register the fact of revisitation,
but is unable to identify any personal user data. Exceptions are the cases where
the user himself communicates certain data by filling registration forms at the site;
however, even in this case such data are extremely rarely stored directly in cookies.
As a rule, these data are saved in the web server’s database. However, it all depends on
the web programmers who create the sites visited by the user: below is the description
of the utility program which helps the user verify cookies on his computer.
2.6.4 Data Leakage Paths and Hazards Created by Cookies
There are several typical ways through which the information stored in cookies can
be obtained by intruders: