

2 Secure Implementation of Lattice-Based Encryption Schemes
45
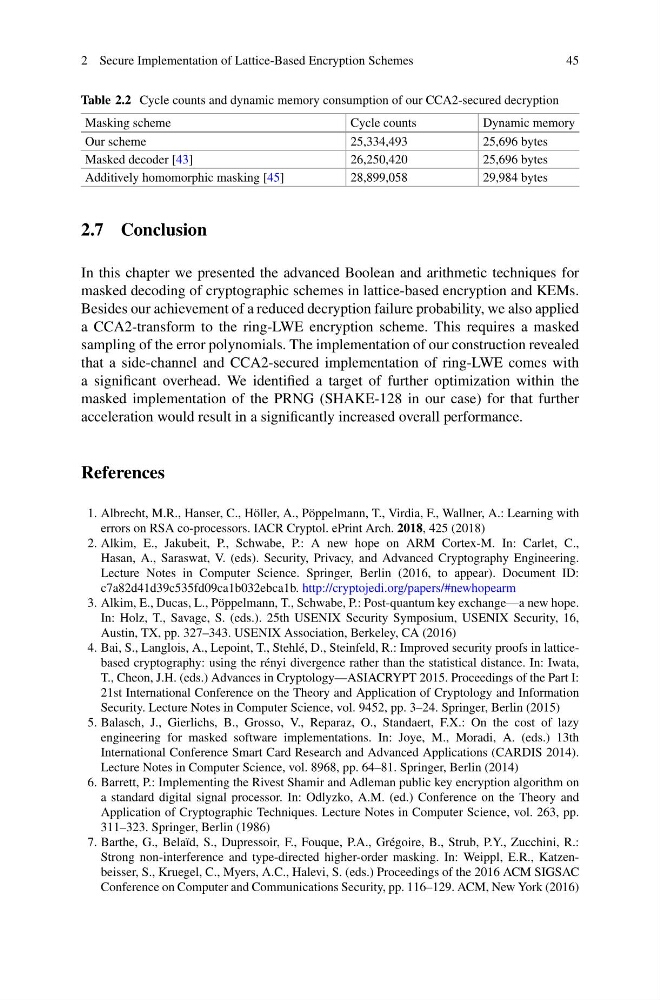
Table 2.2 Cycle counts and dynamic memory consumption of our CCA2-secured decryption
Masking scheme
Cycle counts
Dynamic memory
Our scheme
25,334,493
25,696 bytes
Masked decoder [43]
26,250,420
25,696 bytes
Additively homomorphic masking [45]
28,899,058
29,984 bytes
2.7 Conclusion
In this chapter we presented the advanced Boolean and arithmetic techniques for
masked decoding of cryptographic schemes in lattice-based encryption and KEMs.
Besides our achievement of a reduced decryption failure probability, we also applied
a CCA2-transform to the ring-LWE encryption scheme. This requires a masked
sampling of the error polynomials. The implementation of our construction revealed
that a side-channel and CCA2-secured implementation of ring-LWE comes with
a significant overhead. We identified a target of further optimization within the
masked implementation of the PRNG (SHAKE-128 in our case) for that further
acceleration would result in a significantly increased overall performance.
References
1. Albrecht, M.R., Hanser, C., Höller, A., Pöppelmann, T., Virdia, F., Wallner, A.: Learning with
errors on RSA co-processors. IACR Cryptol. ePrint Arch. 2018, 425 (2018)
2. Alkim, E., Jakubeit, P., Schwabe, P.: A new hope on ARM Cortex-M. In: Carlet, C.,
Hasan, A., Saraswat, V. (eds). Security, Privacy, and Advanced Cryptography Engineering.
Lecture Notes in Computer Science. Springer, Berlin (2016, to appear). Document ID:
c7a82d41d39c535fd09ca1b032ebca1b. http://cryptojedi.org/papers/#newhopearm
3. Alkim, E., Ducas, L., Pöppelmann, T., Schwabe, P.: Post-quantum key exchange—a new hope.
In: Holz, T., Savage, S. (eds.). 25th USENIX Security Symposium, USENIX Security, 16,
Austin, TX, pp. 327–343. USENIX Association, Berkeley, CA (2016)
4. Bai, S., Langlois, A., Lepoint, T., Stehlé, D., Steinfeld, R.: Improved security proofs in latticebased cryptography: using the rényi divergence rather than the statistical distance. In: Iwata,
T., Cheon, J.H. (eds.) Advances in Cryptology—ASIACRYPT 2015. Proceedings of the Part I:
21st International Conference on the Theory and Application of Cryptology and Information
Security. Lecture Notes in Computer Science, vol. 9452, pp. 3–24. Springer, Berlin (2015)
5. Balasch, J., Gierlichs, B., Grosso, V., Reparaz, O., Standaert, F.X.: On the cost of lazy
engineering for masked software implementations. In: Joye, M., Moradi, A. (eds.) 13th
International Conference Smart Card Research and Advanced Applications (CARDIS 2014).
Lecture Notes in Computer Science, vol. 8968, pp. 64–81. Springer, Berlin (2014)
6. Barrett, P.: Implementing the Rivest Shamir and Adleman public key encryption algorithm on
a standard digital signal processor. In: Odlyzko, A.M. (ed.) Conference on the Theory and
Application of Cryptographic Techniques. Lecture Notes in Computer Science, vol. 263, pp.
311–323. Springer, Berlin (1986)
7. Barthe, G., Belaïd, S., Dupressoir, F., Fouque, P.A., Grégoire, B., Strub, P.Y., Zucchini, R.:
Strong non-interference and type-directed higher-order masking. In: Weippl, E.R., Katzenbeisser, S., Kruegel, C., Myers, A.C., Halevi, S. (eds.) Proceedings of the 2016 ACM SIGSAC
Conference on Computer and Communications Security, pp. 116–129. ACM, New York (2016)