

201
Review on Communication Security Issues in IoT Medical Devices
In this formula, b, d, a, and c are real numbers. To generate different elliptic curves, we
can change the values of “a” and “c.” Public key is generated by scalar multiplication with
consistent base point G in the elliptic curve, whereas private key is generated by random
number generations. Little key size in ECC is a greatly favored option. Comparing with
1024 key size in RSA algorithm, ECCs of 160 bit key size is equal.
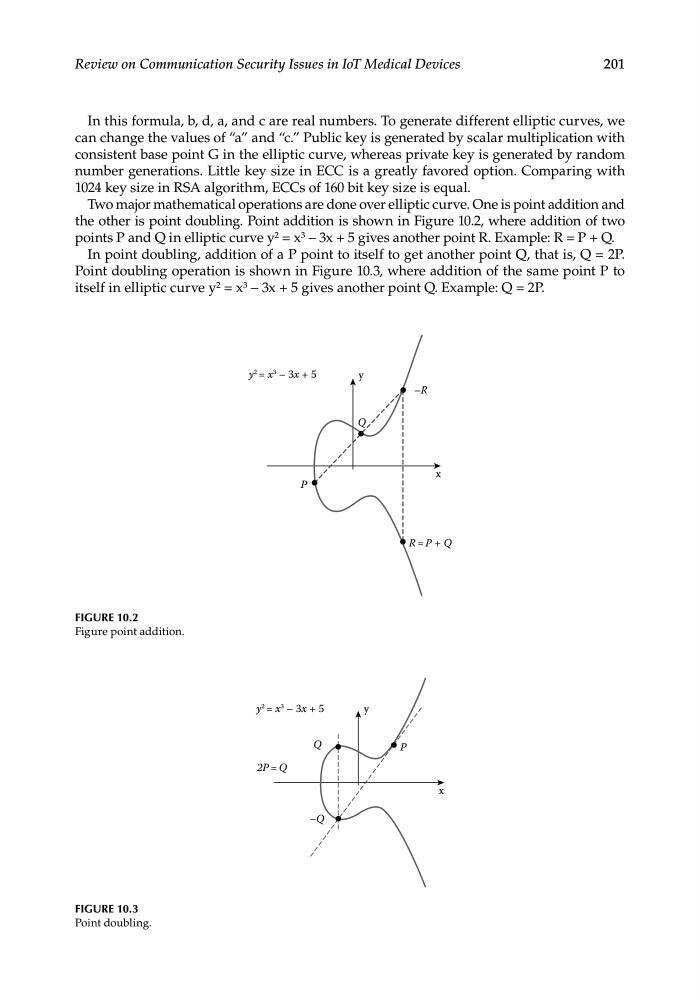
Two major mathematical operations are done over elliptic curve. One is point addition and
the other is point doubling. Point addition is shown in Figure 10.2, where addition of two
points P and Q in elliptic curve y 2 = x 3 − 3x + 5 gives another point R. Example: R = P + Q.
In point doubling, addition of a P point to itself to get another point Q, that is, Q = 2P.
Point doubling operation is shown in Figure 10.3, where addition of the same point P to
itself in elliptic curve y 2 = x 3 − 3x + 5 gives another point Q. Example: Q = 2P.
y
y
2 = x
3 – 3x + 5
x
–R
Q
P
R = P + Q
FIGURE 10.2
Figure point addition.
Q
P
–Q
2P = Q
y
2 = x
3 – 3x + 5
y
x
FIGURE 10.3
Point doubling.